Why execution trust matters.
Cybersecurity secures who gets in and what they can access. Execution trust secures what actually happens when a high-risk change is about to execute, with cryptographic proof, not assumed approval.
Book a demoWhat is execution trust?
Execution trust is cryptographic proof, at the moment a high-risk change would execute, that its authorized signers approved this exact change.
Digital Trust Foundry sits inside the cybersecurity story, not as a new product category, but as the layer that closes this gap.
Cybersecurity's blind spot
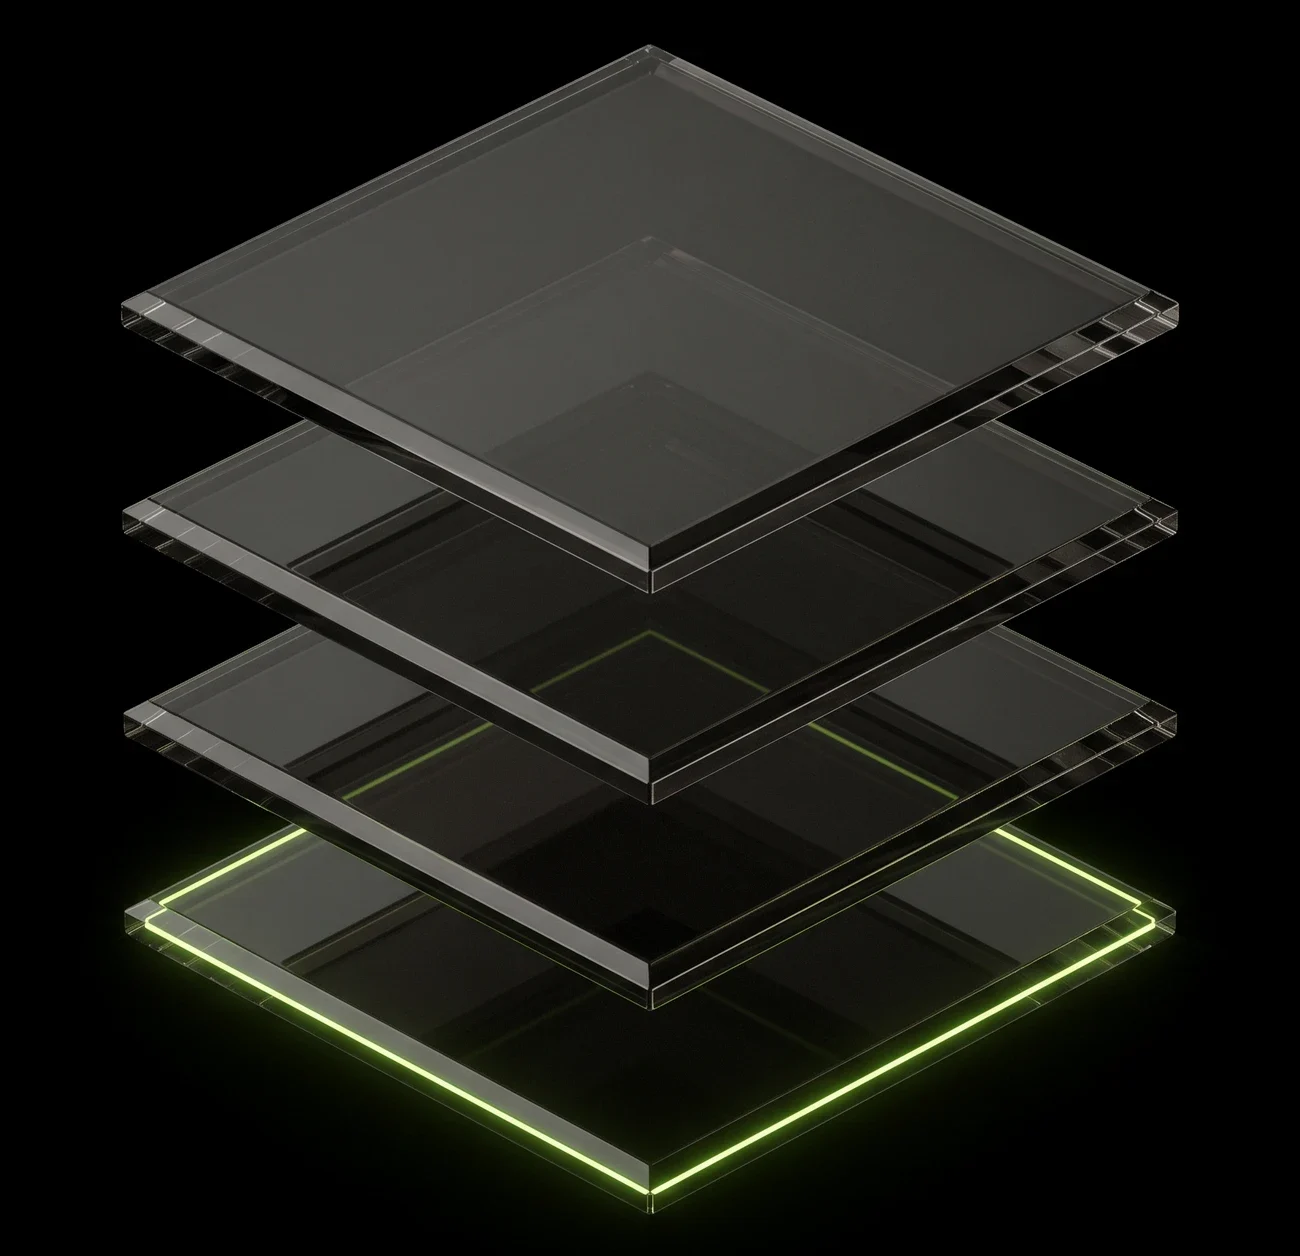
Organizations secured login, network, and device. They did not secure the payee change, the vendor update, or the compliance attestation at the moment it executes.
01Network and device
Who and what can reach your systems.
02Login
MFA and passkeys: who signed in.
03Access
IAM and Zero Trust: what a session may touch.
04The change itself
The payee change, the vendor update, the attestation, at the moment it executes. Execution trust secures this layer.
Why breaches still happen after MFA and Zero Trust
The attack is a change request, not a broken login.
- Change-control impersonation
- Attackers impersonate a legitimate change request, not a login.
- Business email compromise
- Fraudulent bank-detail updates after users passed authentication.
- Insider action after legitimate login
- The session is trusted; the specific change is not verified.
What execution trust adds
Before a high-risk action executes, Foundry verifies that:
- The artifact is authentic and has not been tampered with.
- The necessary authorized signers approved this exact change.
- Policy (dual control, thresholds, roles) was satisfied.
- Proof can be verified independently later, by auditors, regulators, or relying parties.
Why now
Enterprises can no longer rely on assumed trust, static credentials, or network-based controls. They need cryptographic proof of identity, authority, and artifacts at the moment of execution.
AI agents, automation, and cross-organizational workflows now drive core operations, yet identity systems still rely on credentials designed for human logins, not autonomous execution.
Works with your stack
Foundry complements MFA, passkeys, IAM, CA/PKI document signing, and Zero Trust. It does not replace them.
ServiceNow and Salesforce integrations are available now. The same Trustables API pattern applies to any application platform. Regulated tenants can add the optional Forensic Audit Console for investigation-grade trails.
How we're better than MFA, PKI, and Zero Trust alone